We find it before someone else does. Hivexia runs penetration tests against the systems
you actually depend on, and hands you findings your engineers can act on, not a scanner
export with the logo changed.
GET /api/v1/invoices/40112 HTTP/1.1
Host: portal.example.com
Cookie: session=<account A>

HTTP/1.1 200 OK
{"id":40112,"customer":"<account B>",
 "vat":"5*******","total":"1 480,00"}
Remediation. Authorise every record server-side against the session owner. An
identifier in the path is a request, not a permission.
What we do
Find it, close it, stop the next one.
Eighteen services and one open door, but only one argument. Most clients start in the
first column and move right as the obvious problems get fixed.
01 · Identify
Find what is already there
Controlled attacks against your real systems, with every finding exploited and
validated by hand before it reaches your report.
Some of the work we are proudest of did not fit a category when it arrived. We have
tested smart TV applications, and we regularly look at targets we have never seen
before.
Describe what you have. We will tell you what a test would look
like and what it would cost, or tell you plainly that we are not the right people for
it. Both answers are worth having.
Smart TV applications
Set-top boxes
Embedded and IoT devices
Kiosks and point of sale
Desktop applications
APIs and integrations
Hardware and firmware
Industrial protocols
Engagements
What you are actually buying.
Most work is a fixed-scope test at a fixed price. What changes between clients is what
we count to size it, and that count is what both sides can hold each other to later.
Scoped by
Web application test
URLs · applications · user roles
External infrastructure test
Public IP addresses · exposed services
Internal network and Active Directory
Servers · domains · network segments
Mobile application test
Applications · platforms · APIs
Phishing campaign
Users with email accounts
Continuous vulnerability management
Assets under watch · monthly cycles
Scoped in countable things
Twenty IP addresses, sixty-five URLs, three user roles. If we cannot count it we
cannot quote it honestly, and you cannot check afterwards that you got it.
Fixed price, agreed up front
Once the scope is set, the price is set. If we find the environment is materially
larger than described, we come back to you before doing the work, not after.
The retest is part of it
Validating your fixes is included in the original price. A finding you have closed
should not cost you again to prove closed.
What you receive
The report is the product.
Buyers are told to ask every vendor for a sample report before signing, and most cannot
produce one. Here are real pages, with the client name, hostnames and reference
anonymised.
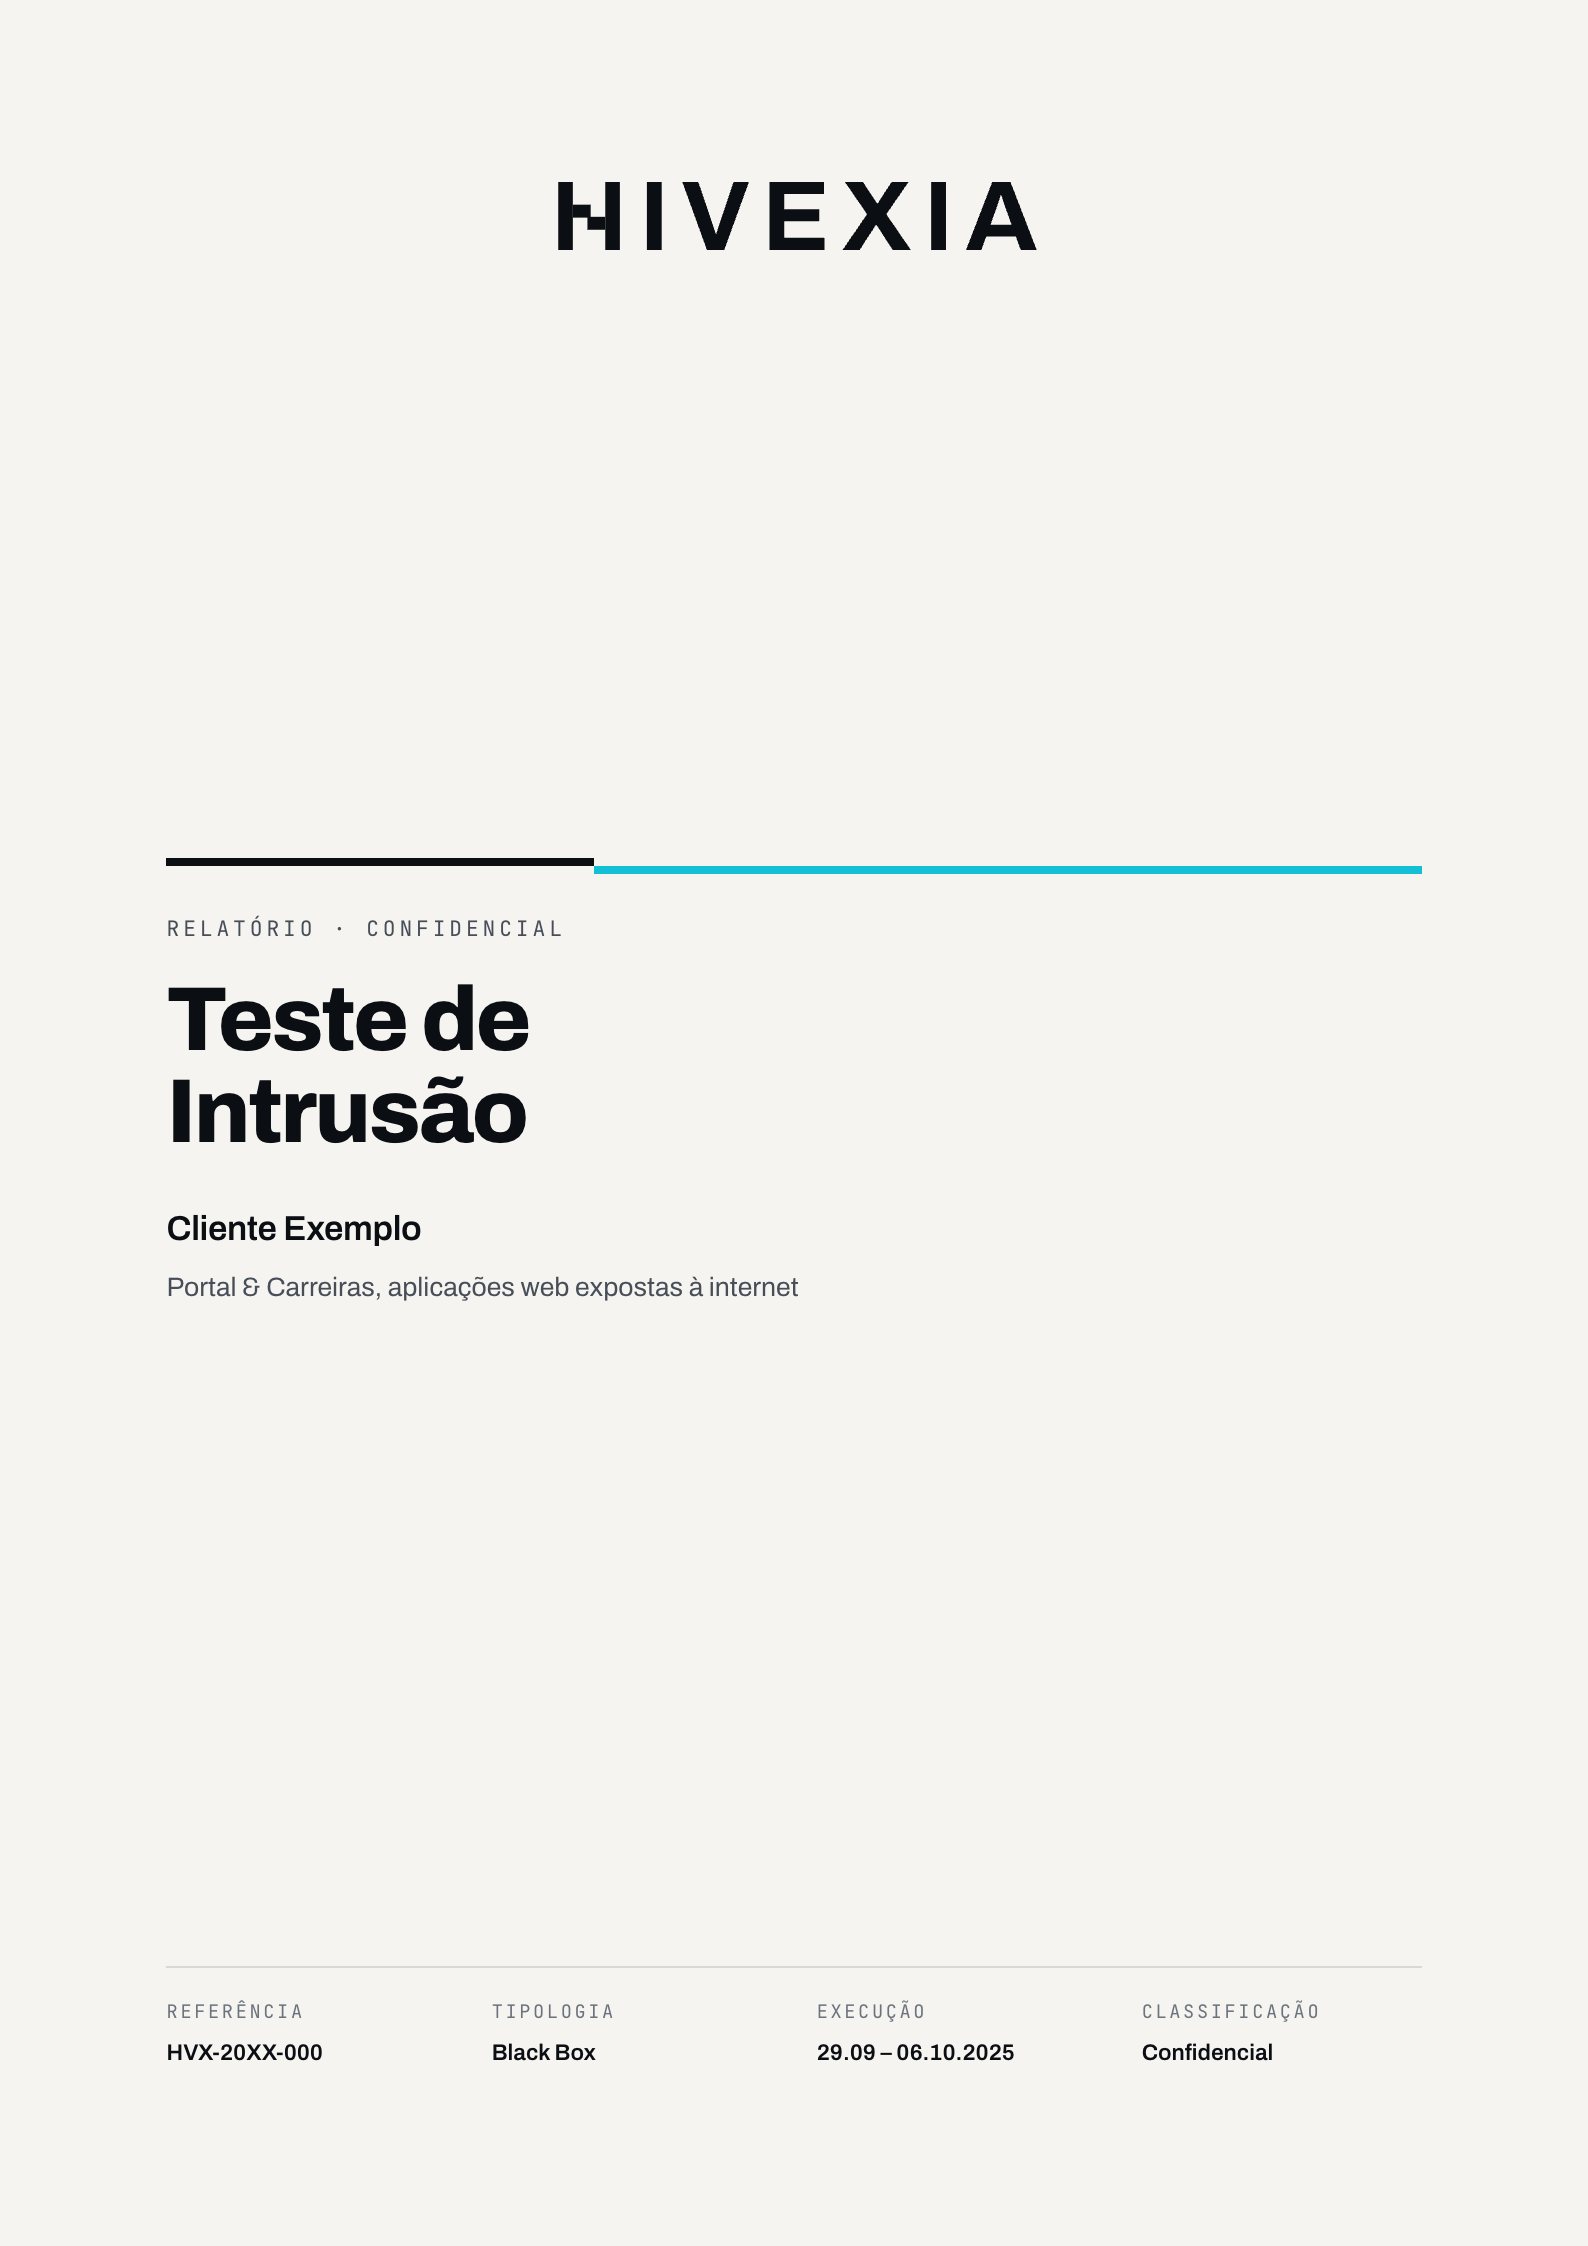
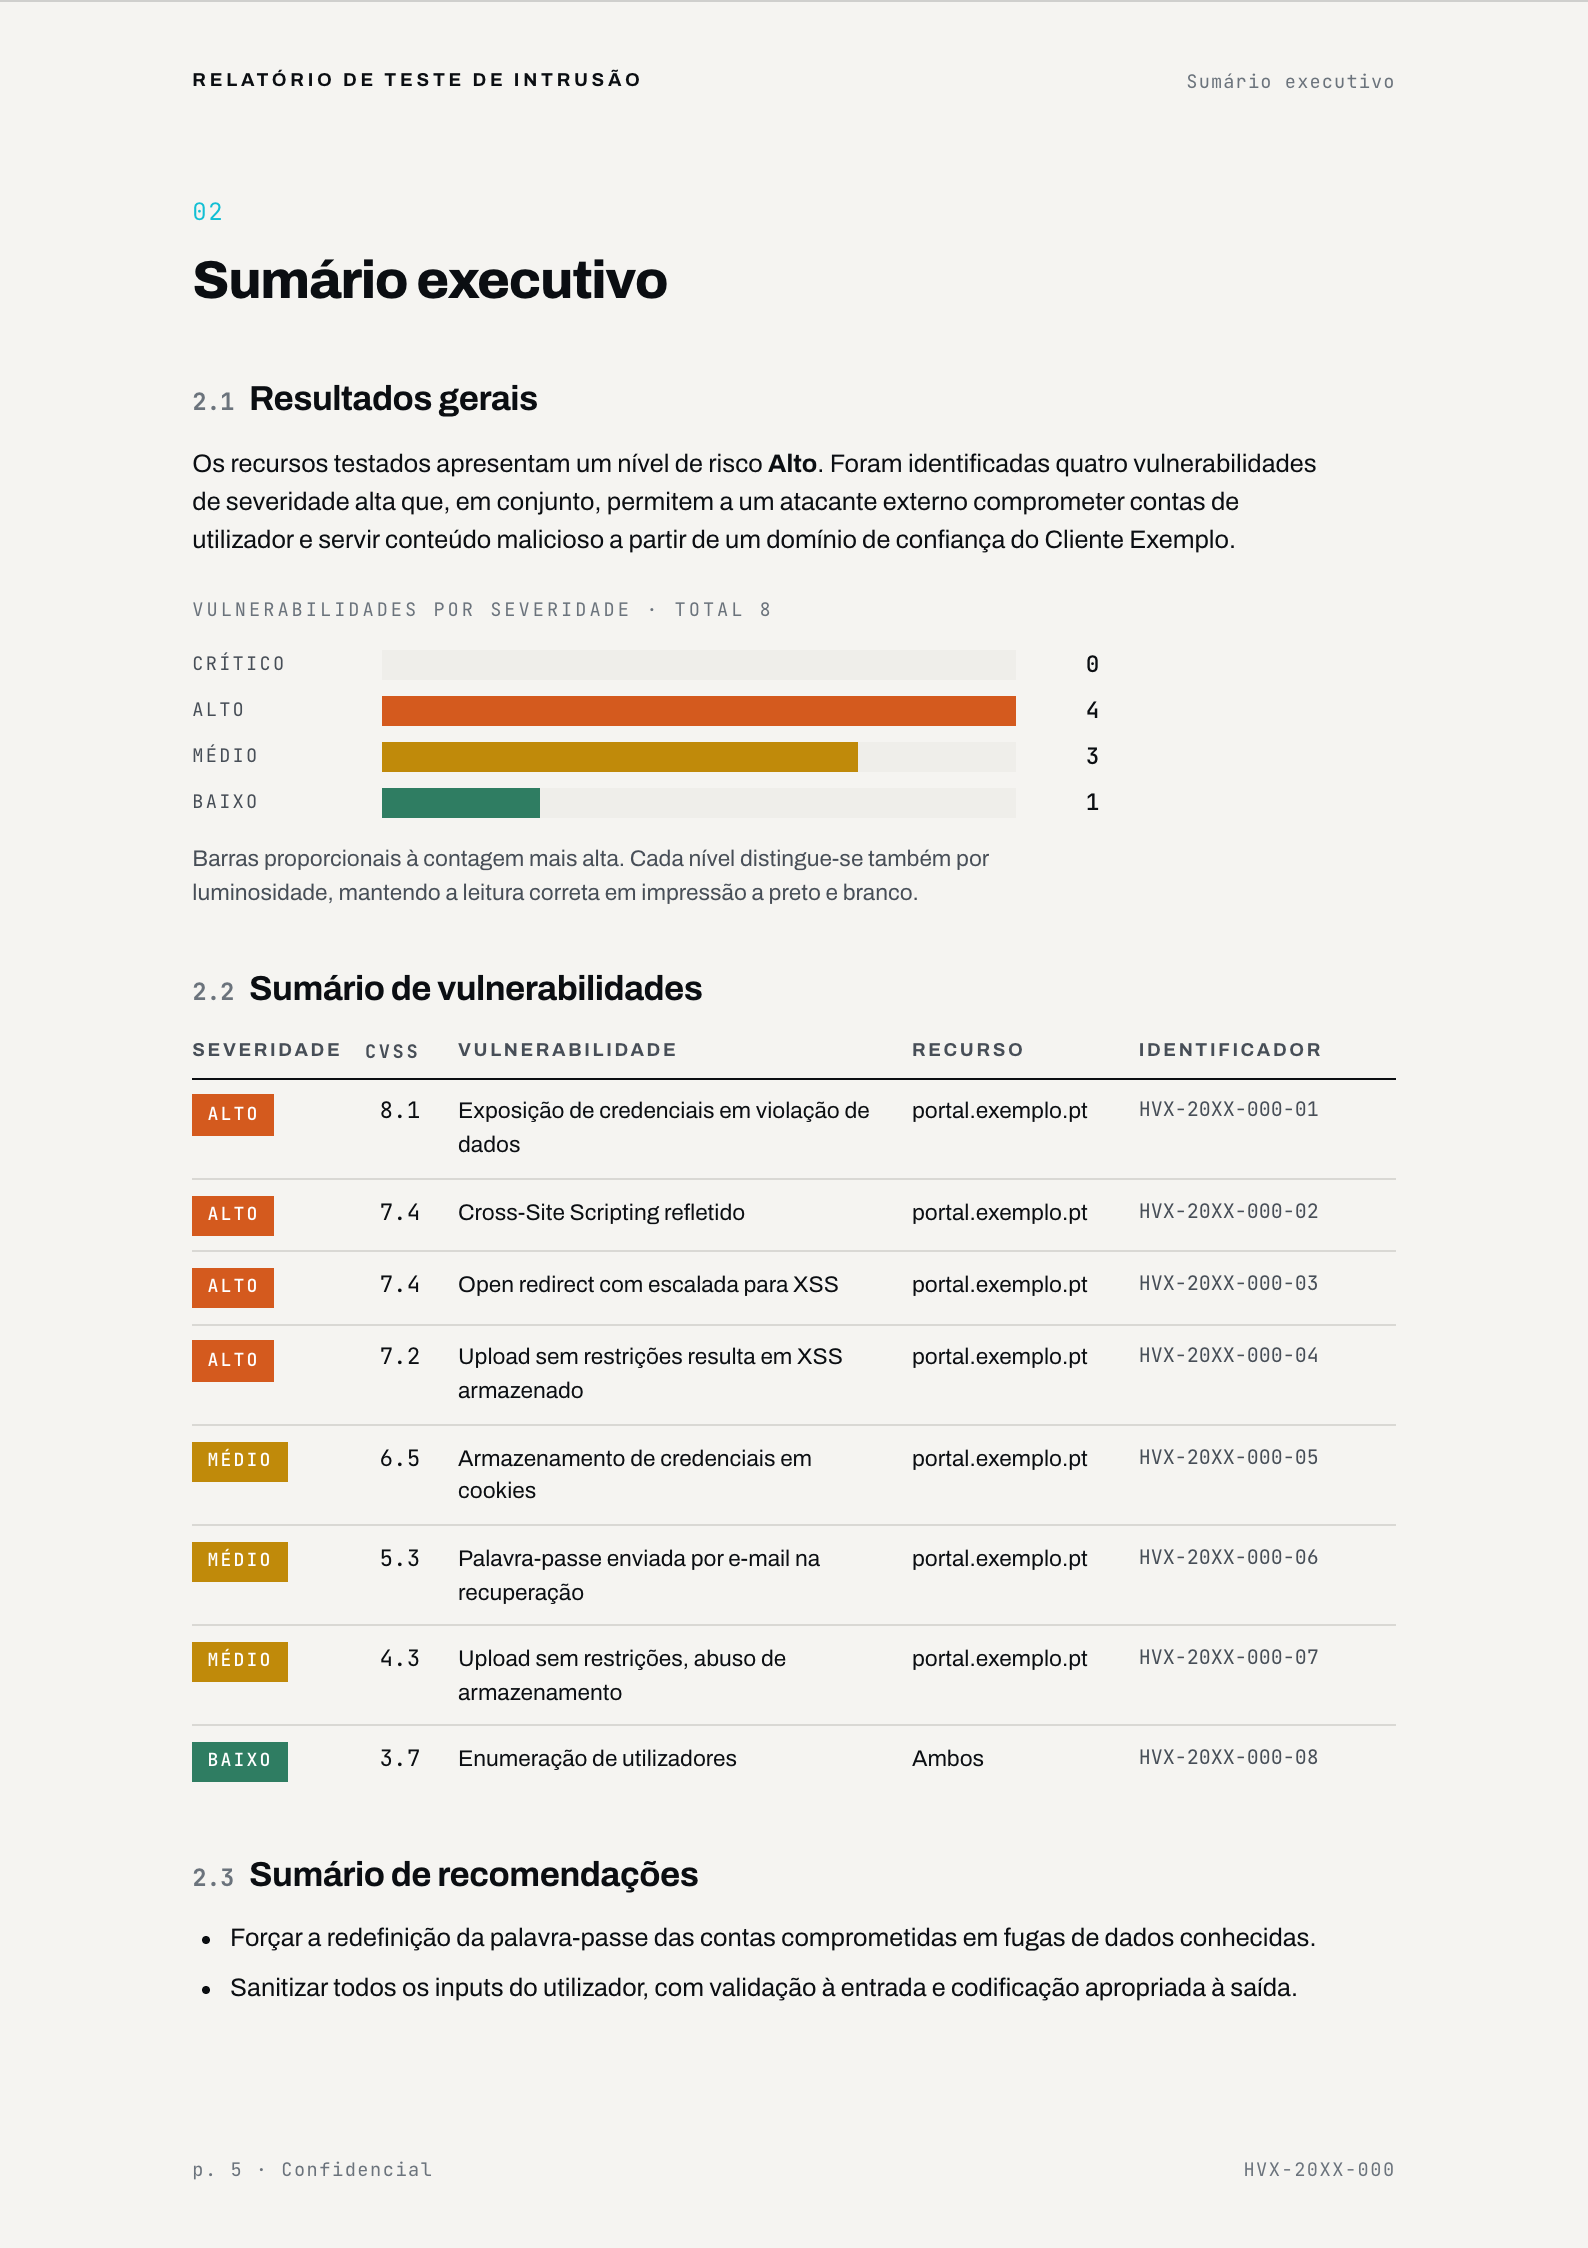
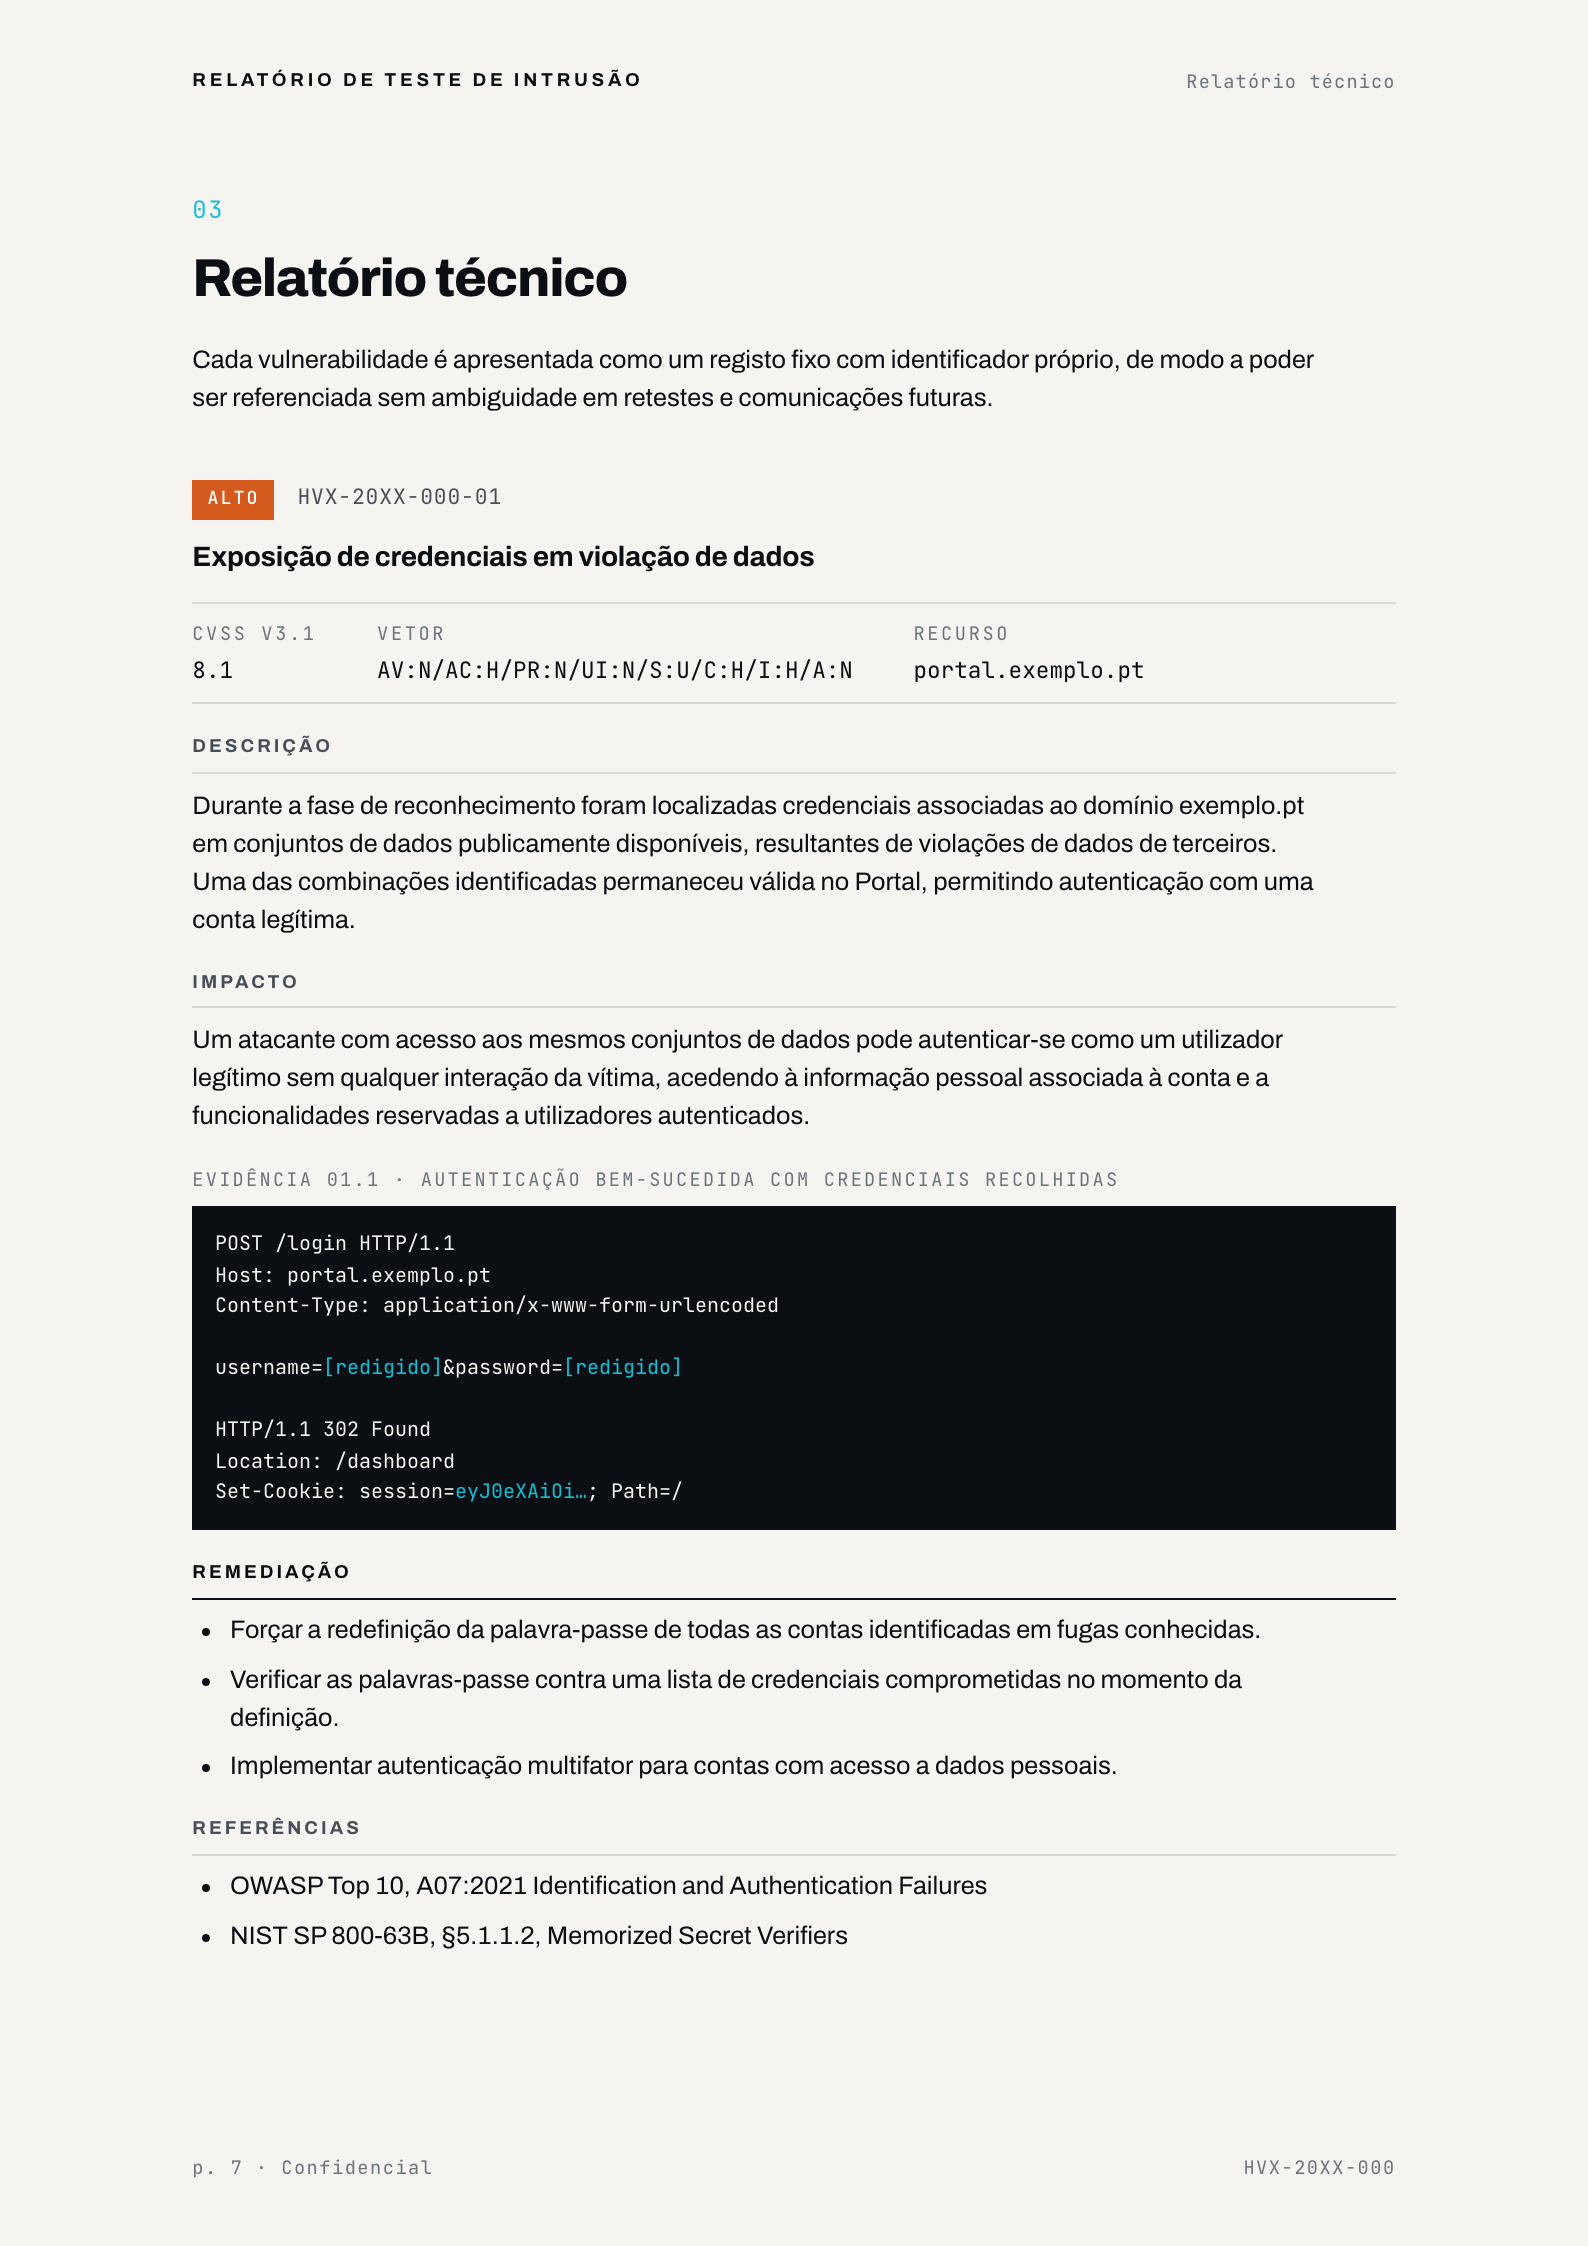
CoverExecutive summaryFinding record
Every finding carries a permanent identifier in the form HVX-20XX-000-03,
so it can be referenced without ambiguity in retests, audits and correspondence with third
parties. Reports are delivered in Portuguese or English. The pages above are from a 2025
engagement scored under CVSS v3.1; current engagements are scored under v4.0.
Executive reportFor management. Risk level, severity distribution, and where to spend first.
Technical reportFor your engineers. One record per vulnerability with a permanent identifier, CVSS score and vector, evidence, and remediation.
Remediation listEvery action ordered by the risk it removes, not by the order we found things.
Results sessionWe walk your teams through the findings and answer questions live.
RetestValidation after your fixes, issued as an addendum that keeps the original numbering.
Severity is scored, not asserted
Crítico9.0 – 10.0
Alto7.0 – 8.9
Médio4.0 – 6.9
Baixo0.1 – 3.9
Credentials
Ten years of this, and the certifications to match.
Our team has worked across web, network and operational technology, including ICS
environments where few providers have validated competence. You are told who runs your
engagement before it starts.
Offensive
OSCP Offensive Security Certified Professional
eWPTX Web Application Penetration Tester eXtreme
eCPPT Certified Professional Penetration Tester
eJPT Junior Penetration Tester
BSCP Burp Suite Certified Practitioner
Governance and data
EXIN Information Security Management ISO/IEC 27001
EXIN Data Protection Officer
EXIN Privacy & Data Protection Professional
Platform
AWS Certified Cloud Practitioner
Sophos Certified Architect
Sophos Certified Engineer
Tell us what you need tested.
A scoping call takes about thirty minutes. Bring the systems you are worried about and
we will tell you honestly whether a test is the right next step.